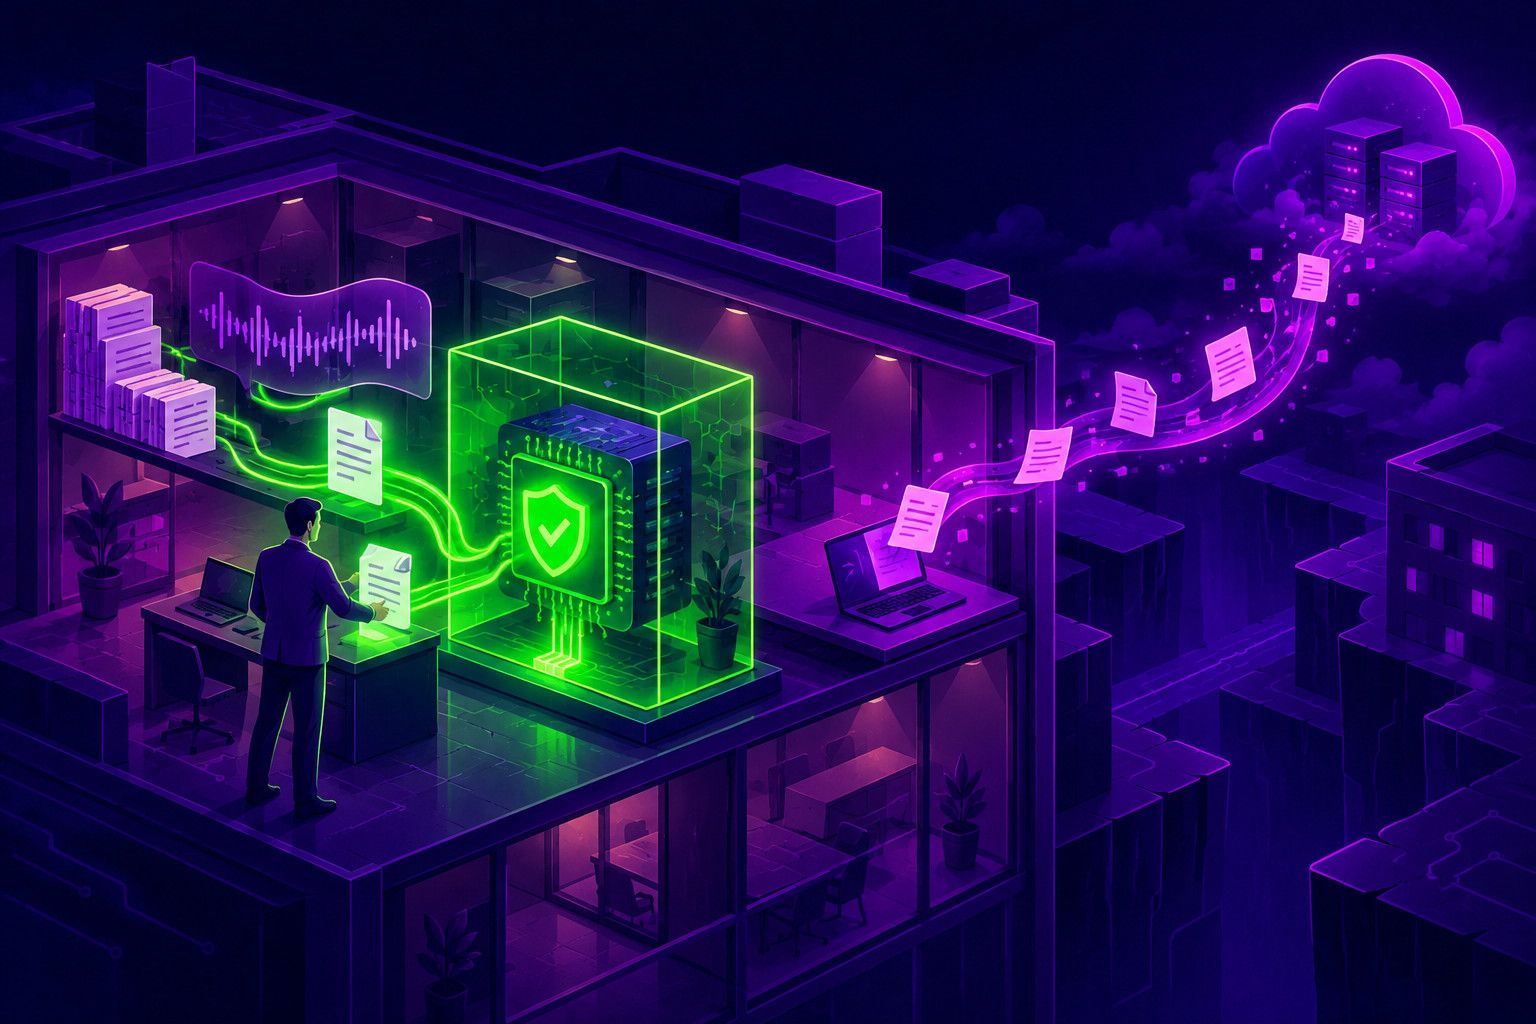
A solicitor pastes a draft letter into a chatbot to tidy the wording. An HR manager uploads the recording of a grievance meeting to get the minutes written. A clinician asks a free tool to summarise a referral. Each of them is trying to do a good job faster, and each of them has just sent confidential information to a company their organisation has no contract with.
This is “shadow AI”: people using AI tools their organisation has not approved, often on personal accounts. This article sets out how common it is, why it matters for anyone who handles sensitive information, and why the answer is no longer a ban but a better alternative.
It is already happening
- In Microsoft and LinkedIn’s 2024 survey of 31,000 people, 75% of knowledge workers said they used generative AI at work, and 78% of those users brought their own AI tools to work Microsoft.
- In a 2025 survey of UK employees for Microsoft, 71% had used unapproved consumer AI tools at work and 51% did so every week. Only 32% were concerned about the privacy of the company or customer data they entered, and 28% said their employer offered no approved option Microsoft UK.
- Cyberhaven, which monitors data movement, found that 11% of what employees pasted into ChatGPT was confidential Cyberhaven.
- Netskope’s 2026 report found that breaches of organisations’ data policies involving generative AI had more than doubled in a year, to an average of 223 a month per organisation Netskope.
These are vendor surveys and figures, and they vary. They all point the same way: the question is not whether your people are using AI with your data, but how much.
Why it matters
The data is out of your control
When Samsung engineers pasted confidential source code into ChatGPT in 2023, the company banned generative AI on its devices. Its concern was that data held on external servers is hard to retrieve or delete, and could be disclosed to others Bloomberg.
It costs more when it goes wrong
IBM’s 2025 study of data breaches found that one in five organisations had suffered a breach involving shadow AI, and that high levels of it added around US$670,000 to the average cost of a breach. 63% of the organisations breached had no policy governing AI, or were still writing one IBM.
Your obligations do not change
You remain responsible for personal data you process, whoever’s tool you process it in. Sending it to a provider overseas still needs a lawful basis, a transfer mechanism and an assessment of the risk. The Data (Use and Access) Act 2025 has changed the test for international transfers, now in force, but it has not removed the need for one legislation.gov.uk.
For regulated professions, the guidance is explicit:
- The courts. Judicial guidance tells judges not to enter private or confidential information into public AI chatbots, and to treat anything entered as though it may become public Courts and Tribunals Judiciary.
- The Bar. The Bar Council’s updated guidance lists the risks of confidential information being used to train AI systems Bar Council, and the Law Society’s guidance for solicitors covers the same ground Law Society.
- Health and care. NHS England’s guidance on AI transcription in health and care requires a data protection impact assessment, makes clear the organisation stays accountable for patient data processed by suppliers, and expects clinicians to check what the tools produce NHS England.
Even the regulator applies the rule to itself. The Information Commissioner’s Office allows its own staff to use only AI tools it has approved, and restricts their use with personal or confidential information ICO.
Banning it does not work
Samsung’s ban was a reasonable first reaction, but bans on useful tools rarely hold. When more than a quarter of staff say they use consumer tools because their employer offers nothing else, a ban without an alternative simply moves the activity out of sight. The durable answer is to give people an approved tool that is at least as good, and that keeps sensitive data inside.
Private AI is now good enough
Until recently that was hard, because the best AI models were only available as cloud services from a handful of providers. That has changed.
- Stanford’s AI Index found that the gap between the best closed models and the best open models, which anyone can run on their own hardware, had narrowed from 8% to 1.7% on a widely used benchmark between January 2024 and February 2025, while the cost of running a model of a given capability had fallen more than 280-fold in two years Stanford HAI.
- Open speech recognition such as OpenAI’s Whisper, trained on 680,000 hours of audio, can transcribe recordings without them leaving your network arXiv.
- Open translation models such as Meta’s NLLB-200 cover 200 languages in a single model arXiv.
For transcription, translation and asking questions of your own documents, the most common reasons staff reach for public tools, private AI running on your own infrastructure is now capable, affordable and fast. For sensitive work, it should be the default.
What to do on Monday
- Find out what is being used. Your network and data-loss prevention logs will show which AI tools are in use, and on which accounts.
- Publish a short, clear policy. List the approved tools, and the information that must never go into a public one: client, patient, personnel and legally privileged material.
- Provide an approved alternative, at least as good as the tools people are using now.
- Assess every AI supplier properly, with a data protection impact assessment and, for overseas providers, a transfer risk assessment.
- Keep the most sensitive work in-house, on infrastructure you control, or contractually forbid suppliers from retaining or training on your data.
- Keep a person checking the output, and record where AI was used.
- Treat an accidental disclosure as a data incident, and make it easy and safe to report.
If you handle sensitive information and want your people to use AI safely, talk to us. We also make MetaVox, MetaLex and Radiant, for transcription, translation and document questions that never leave your network.
Sources
- Microsoft and LinkedIn (2024). 2024 Work Trend Index. Vendor research.
- Microsoft UK (2025). Rise in shadow AI tools raising security concerns for UK organisations. Vendor research.
- Cyberhaven (2023). Workers have pasted company data into ChatGPT. Vendor research.
- Netskope Threat Labs (2026). Cloud and Threat Report: 2026. Vendor research.
- Bloomberg (2023). Samsung bans staff’s AI use after spotting ChatGPT data leak.
- IBM (2025). Cost of a Data Breach report 2025.
- Data (Use and Access) Act 2025. legislation.gov.uk.
- Courts and Tribunals Judiciary (2025). Artificial intelligence (AI): judicial guidance.
- Bar Council (2025). Updated guidance on generative AI for the Bar.
- The Law Society. Generative AI: the essentials.
- NHS England (2025). Guidance on the use of AI-enabled ambient scribing products in health and care settings.
- Information Commissioner’s Office (2025). Internal AI use policy.
- Stanford HAI (2025). AI Index Report 2025.
- Radford, A. and others (2022). Robust speech recognition via large-scale weak supervision.
- NLLB Team (2022). No Language Left Behind: scaling human-centered machine translation.
Want to talk this through?
We help organisations put ideas like these into practice. Tell us what you are working on and we will help you find a practical next step.